Clearly AI Moves Security Reviews Upstream
Automation handles repetition, not accountability
By WhatAI Editorial Team ·
Security review is one of those enterprise processes that everyone agrees should happen early and few organizations can perform at the speed engineering now moves. A feature begins as a ticket, expands into architecture notes, code, vendor choices, data flows, and launch dependencies, then reaches a small security or privacy team with a deadline already attached. The reviewer spends days reconstructing context before the real risk conversation can begin.
Clearly AI is built around that bottleneck. It connects to the systems where product work already lives, ingests an organization's own policies and standards, assesses new products, features, vendors, or AI uses against those requirements, and presents prioritized findings for a human reviewer. Its central promise is not that a language model can replace a security engineer. The company states the opposite in unusually direct language: AI augments, humans decide.
That distinction makes Clearly AI more interesting than another generic security chatbot. The platform is trying to turn review knowledge into an operational system. Threat modeling, privacy impact assessments, AI risk reviews, vendor assessments, triage, and audit documentation become connected workflows rather than separate queues of forms and meetings.
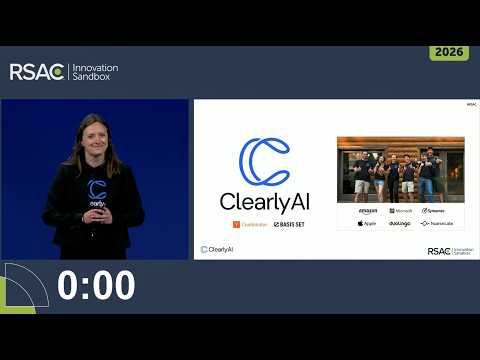
The company is also entering a more demanding phase. Clearly AI announced an $8.4 million seed round in 2026 and says it is already used by large organizations including Ericsson, Rivian, HID Global, Affirm, Webflow, and Okta. Those are company claims, but they signal the intended market clearly. This is enterprise infrastructure sold through a demo and implementation process, not a self-serve app for an individual developer.
The product is a review layer, not a magic scanner
Clearly AI sits upstream of many tools people normally associate with application security. A static analyzer examines code patterns. A software composition tool tracks dependencies. A cloud scanner finds configuration and exposure problems. A runtime platform watches systems in operation. Clearly AI is aimed at the reasoning-heavy review that asks what is being built, which assets and actors are involved, how data moves, which policies apply, and what needs to change before approval.
For threat modeling, the platform can analyze design documentation or code and apply frameworks such as STRIDE, PASTA, or MAESTRO. It can generate diagrams, surface threats, and centralize findings. That can remove a large amount of mechanical work: reading scattered documents, redrawing architecture, translating descriptions into a consistent model, and transferring findings into a tracking system.
It does not make every finding true. A model can misunderstand an architecture, invent a data flow, miss an implicit trust boundary, or apply a policy to the wrong component. A generated diagram is useful because a reviewer can correct it, not because the act of generation proves completeness. Threat modeling remains a structured argument about a system, its assumptions, and plausible abuse paths.
The same principle applies to privacy. Clearly AI supports PIAs, DPIAs, third-party privacy assessments, regulatory reviews, and AI governance evaluations. Automation can collect repeated facts, identify missing answers, map stated practices to a policy, and draft structured documentation. The accountable privacy team still has to interpret purpose, necessity, proportionality, consent, residency, retention, and local law in the context of the actual deployment.
Connect, ingest, automate, review
Clearly AI describes its platform in four steps. First, connect the systems teams already use, with Jira, GitHub, Confluence, and Google Drive named publicly. Second, ingest the organization's policies, standards, security requirements, and review knowledge. Third, automate assessments of each new feature, product, or vendor. Fourth, let the responsible team review the prioritized findings and make the decision.
The order matters. A generic model knows common security vocabulary, but an enterprise review is governed by local decisions. One company may prohibit a data flow another accepts. A financial-services team may require evidence that is irrelevant to an internal productivity tool. An automotive product, healthcare workflow, and consumer website can share a framework while carrying different safety, regulatory, and operational consequences.
Policy ingestion is therefore the centre of the product's value and one of its largest implementation risks. If the source material is contradictory, obsolete, or scattered across unofficial documents, automation will reproduce that uncertainty at scale. A successful deployment needs policy owners, authoritative versions, applicability rules, exceptions, and an update process. Uploading a folder is not the same as creating a dependable control library.
Integration quality matters just as much. A Jira ticket may contain the business intent but not the final architecture. A pull request may show code without the decision history. Confluence may contain a diagram that no longer matches production. Google Drive may hold approved standards beside working drafts. Clearly AI can reduce the effort of gathering context, but the organization must decide which system is authoritative for each fact.
The review stage is where accountability stays visible. The product can prioritize findings and prepare documentation, but a security, privacy, or GRC professional accepts, rejects, modifies, or escalates the recommendation. That review should be recorded. If a team cannot later explain which inputs, policy version, model output, reviewer, and exception produced an approval, faster automation may weaken rather than improve governance.
Threat modeling can become continuous
Traditional threat modeling often happens at one of two bad times: as a workshop before the design is concrete or as a gate after implementation is expensive to change. Clearly AI's integration model makes a more continuous approach possible. A new feature or material change can trigger a review while the ticket, design, and code are still active. Findings can travel back into the engineering workflow instead of becoming a detached report.
This is a better use of AI than asking it for a complete threat list from a paragraph. The model can gather context from several artifacts, apply a selected methodology consistently, create a first-pass diagram, and identify where information is missing. The reviewer can spend more time on unusual attack paths, business consequences, compensating controls, and the parts of the design that do not fit a template.
Consistency is valuable in large organizations. Two security engineers may reasonably emphasize different risks. A common workflow and policy base can make routine coverage more repeatable without erasing expert judgment. It can also reveal where teams disagree, since exceptions and edits become data that can improve future reviews.
Yet continuous review can become continuous noise. If every small ticket produces a long threat model, engineers will learn to ignore findings. A deployment needs triage rules that distinguish cosmetic changes from material changes, apply the right review depth, suppress known false positives, and route only actionable issues. Review coverage should increase without turning the security team into a machine-output cleanup service.
Privacy, AI governance, and vendor risk share the queue
Clearly AI's broader opportunity is that enterprise reviews overlap. A new AI feature may need product-security analysis, a privacy impact assessment, an AI governance review, vendor due diligence, data-residency checks, and evidence for an audit. Treating each as an isolated questionnaire forces business owners to repeat context and leaves reviewers reconciling different answers manually.
A shared platform can reuse source documentation and route the same facts through different control sets. In Clearly AI's published Ericsson case study, the customer says 85 percent of vendor assessments are now completed from source documentation without a business owner filling in every question. The same case study reports a 50 to 80 percent reduction in review time across assessment types. These are customer outcomes presented by the vendor, not controlled benchmarks, but they illustrate the workflow Clearly AI is selling.
The benefit is not simply speed. Reusing evidence can reduce conflicting answers, make gaps visible, and create more consistent records for audit. It can also free a specialist to investigate exceptions rather than transcribe information from one form to another. For organizations with hundreds of products and vendors, that administrative difference can determine whether review coverage remains selective or becomes systematic.
The risk is inappropriate reuse. A vendor's public security page may support an initial assessment but not prove that a specific control operates in the contracted environment. A previous product answer may be stale after an architecture change. A privacy statement written for one jurisdiction may not satisfy another. Automation should preserve the source, date, scope, and confidence of reused evidence instead of converting every document into an undifferentiated fact base.
AI risk review adds another layer. A team needs to know which model is used, what data enters it, where prompts and outputs are stored, whether providers train on customer content, which actions are automated, how people can challenge decisions, and how failures are monitored. Clearly AI can make that assessment repeatable, but the organization's AI policy must define its own thresholds and prohibited uses first.
Human in the loop must mean more than a button
Security vendors often use human in the loop as a reassurance phrase. The important question is what the human can actually see and change. A reviewer needs the relevant source context, applicable policy, reasoning or evidence behind a finding, confidence or uncertainty, and a way to correct the model. They also need an escalation path when the platform cannot resolve an ambiguity.
Approval design matters. If the interface encourages reviewers to accept a large batch quickly, the human becomes a ceremonial signer. If every low-risk issue requires detailed manual handling, the automation fails to create capacity. The control should match the consequence: low-risk, well-defined checks can be highly automated; novel architectures, sensitive data, safety implications, and regulatory uncertainty need deeper expert attention.
Organizations should also separate model quality from workflow quality. Even an imperfect first pass can be valuable if it consistently gathers facts, exposes missing information, and shortens preparation. A model with impressive prose can be dangerous if it hides unsupported assumptions. The evaluation should measure correction effort, missed critical risks, false-positive burden, policy alignment, and final review quality, not how polished the generated report appears.
Clearly AI's published case studies report large reductions in review time and backlogs. Buyers should ask how each number was defined: which review types were included, what the previous process required, how many products were assessed, what level of human review remained, and whether risk outcomes improved. Time saved is meaningful only when coverage and decision quality remain acceptable.
Pricing is part of the enterprise conversation
Clearly AI does not publish a self-serve price list or free plan. The website directs prospective customers to book a demo, and pricing appears to be configured around organizational scope, integrations, review types, implementation, volume, and support. Any record that assigns the platform a $0 enterprise tier or a generic $29 to $149 subscription is inventing certainty that the vendor does not provide.
Custom pricing is reasonable for an enterprise platform with policy ingestion and workflow integration, but it makes comparison harder. Buyers should ask for the complete first-year and steady-state cost: platform subscription, implementation, integration work, migration, policy normalization, training, premium support, additional environments, data residency, private deployment, and usage-based limits if any.
The economic case should be tied to the current review system. Measure the number and type of reviews, median queue time, specialist hours, engineering interruption, percentage of products reviewed, rework, audit preparation, and incidents caused by missed requirements. Then pilot Clearly AI on a representative sample. Savings created by automating simple assessments should not be extrapolated to every complex review.
A mature team may justify the platform by increasing coverage rather than reducing headcount. If only a small share of products receives meaningful review today, automation can help the same team reach more of the portfolio. That benefit should be reported honestly: more reviewed changes, earlier findings, and better evidence may be more valuable than a dramatic labour-savings claim.
A responsible evaluation
Begin with one review type and a bounded product area. Threat modeling is a logical pilot when the organization already has a methodology and known backlog. Privacy assessment can work when forms, policies, and decision owners are well defined. Vendor risk is attractive when source-document reuse consumes significant time. Avoid attempting to automate every security, privacy, and GRC workflow at once.
Create a gold set from completed reviews. Include straightforward cases, difficult exceptions, incomplete inputs, outdated documentation, and known false-positive patterns. Ask experienced reviewers to define the material findings and acceptable outcomes before testing the platform. Without a reference, a team can measure speed but not quality.
Configure only authoritative policies and record their owners, versions, jurisdictions, and applicability. Connect the minimum systems required for the pilot. Confirm data handling, retention, access controls, subprocessors, model-provider terms, logging, deletion, residency, and incident-response commitments. Security-review automation itself becomes a sensitive system because it may ingest architecture, code, vulnerabilities, vendor evidence, and internal policy.
Run Clearly AI beside the existing process before allowing it to replace steps. Compare findings, missing context, correction time, severity, consistency, and reviewer confidence. Track whether engineers receive clearer and earlier actions. Sample approved low-risk reviews after automation to detect quiet drift. Keep an explicit fallback for outages, model changes, and unusual cases.
Finally, decide which steps may be automated and which decisions remain named human responsibilities. Document exceptions and use reviewer corrections to improve policy and configuration. A good rollout should make security expertise more available to engineering, not make ownership harder to locate.
The WhatAI view
Clearly AI addresses a real and expensive gap between modern development speed and enterprise review capacity. Its strongest idea is not automated threat modeling in isolation. It is the shared operating layer that brings security, privacy, AI governance, vendor risk, and GRC evidence into the systems where product work already happens.
The product looks best when the organization has mature review knowledge but insufficient capacity to apply it consistently. Policies are documented, specialist owners exist, Jira and GitHub contain meaningful context, and leadership wants broader coverage without turning every launch into a meeting. In that environment, AI can take on preparation, repetition, first-pass analysis, and documentation while experts focus on exceptions and judgment.
It looks less suitable for a small team seeking an inexpensive scanner or a company hoping software will create a security program from nothing. Clearly AI can ingest standards; it cannot decide an organization's risk appetite on its behalf. It can surface threats; it does not replace testing, code analysis, runtime controls, incident response, legal interpretation, or accountable approval.
The phrase that should guide an evaluation comes from Clearly AI's own product page: AI augments, humans decide. Buyers should test whether the platform makes that division real. If it gives reviewers better context, earlier involvement, consistent policy coverage, traceable evidence, and more time for difficult risk decisions, it can become valuable enterprise infrastructure. If the human is reduced to approving fluent output, the backlog may shrink while governance becomes less trustworthy.
Clearly AI automates preparation and first-pass analysis for enterprise security, privacy, AI governance, vendor risk, and GRC reviews. It brings organizational policies and product context into one workflow while leaving final decisions with human reviewers.
How Clearly AI Works in 2026
The platform connects to tools such as Jira, GitHub, Confluence, and Google Drive, ingests internal standards, evaluates products or changes, and returns prioritized findings. Threat modeling can use STRIDE, PASTA, MAESTRO, or internal methods. Pricing is custom and requires a demo.
Is Clearly AI Right for Your Security Team?
Clearly AI is best suited to organizations with established security, privacy, or GRC requirements and enough review volume to justify enterprise integration. It complements rather than replaces code scanning, testing, monitoring, legal analysis, and accountable expert approval.
About Clearly AI
Clearly AI is an enterprise security and privacy review platform that automates preparation, analysis, documentation, and triage across product-development workflows. It connects to tools such as Jira, GitHub, Confluence, and Google Drive; ingests an organization's policies and standards; and assesses products, features, vendors, and AI uses against those requirements. Use cases include threat modeling, security design reviews, privacy impact assessments, DPIAs, AI risk reviews, vendor risk assessments, GRC evidence, and review triage. Prioritized findings remain subject to human review and approval.
Use Cases
Key Features
- ✓ Automated security and privacy design reviews
- ✓ Threat modeling from design documentation or code
- ✓ Support for STRIDE, PASTA, MAESTRO, and custom methods
- ✓ Generated system, data-flow, and threat-model diagrams
- ✓ Privacy Impact Assessments and DPIAs
- ✓ AI governance and AI risk reviews
- ✓ Vendor and third-party risk assessments
- ✓ Security, privacy, and GRC triage workflows
- ✓ Policy, standard, and control-library ingestion
- ✓ Automated assessment of new features, products, and vendors
- ✓ Prioritized findings with human review and approval
- ✓ Centralized finding tracking and remediation support
- ✓ Audit-ready and regulator-oriented documentation
- ✓ Workflow integrations for Jira, GitHub, Confluence, and Google Drive
Pricing
Enterprise
Custom quote
- • Security, privacy, AI risk, and vendor review workflows
- • Enterprise integrations and policy ingestion
- • Implementation and onboarding
- • Pricing based on organizational requirements
- • Demo required; no public self-serve price list
Pricing varies by plan and region — see current pricing.
Plan features change — last updated: 2026-08-25.
Details
Tags
Clearly AI Community Discussions
Explore community discussions. Ask and answer questions on Clearly AI to grow and learn together.
Clearly AI Showcase
Clearly AI — Frequently Asked Questions
What is Clearly AI?
Clearly AI is an enterprise platform for automating security, privacy, AI governance, vendor risk, and GRC review workflows. It gathers product context, applies organizational requirements, drafts structured analysis, and routes prioritized findings to human reviewers.
How does Clearly AI work?
The platform follows a connect, ingest, automate, and review model. Teams connect development and documentation systems, upload policies and standards, automate assessments of products or changes, and have specialists review the resulting findings and make the final decision.
What integrations does Clearly AI advertise?
The public product page names Jira, GitHub, Confluence, and Google Drive, plus other enterprise tools. Buyers should confirm the depth, permissions, data flow, and availability of each required integration during the sales process.
Can Clearly AI automate threat modeling?
Yes. Clearly AI says it can analyze design documentation or code, generate diagrams, identify threats, and centralize findings using STRIDE, PASTA, MAESTRO, or another selected methodology. Human review remains necessary to correct context and judge risk.
Does Clearly AI support privacy reviews?
Yes. Its privacy workflows cover PIAs, DPIAs, third-party privacy assessments, regulatory compliance reviews, and AI governance evaluations. The platform can prepare documentation and surface gaps, while accountable privacy and legal teams retain final interpretation.
Does Clearly AI replace security engineers?
No. Clearly AI explicitly positions the system as augmentation. It automates context gathering, repetitive checks, first-pass analysis, and documentation, while security, privacy, and GRC professionals review findings and make final decisions.
How much does Clearly AI cost?
Clearly AI does not publish a self-serve price list or free plan. The website directs buyers to book a demo, so pricing should be treated as a custom enterprise quote based on scope, integrations, review volume, implementation, security requirements, and support.
Is Clearly AI suitable for small teams?
It is primarily positioned for enterprises with formal review programs and meaningful assessment volume. A small team seeking inexpensive vulnerability scanning, code analysis, or a self-serve threat-model template will likely find the platform too implementation-heavy.
Sources & References
- Clearly AI official website ↗
- Clearly AI platform overview ↗
- Clearly AI documentation ↗
- Clearly AI threat modeling ↗
- Clearly AI privacy impact assessments ↗
- Clearly AI risk reviews ↗
- Clearly AI for security teams ↗
- Clearly AI for privacy teams ↗
- Clearly AI for GRC teams ↗
- Clearly AI Ericsson case study ↗
- Clearly AI seed funding announcement ↗
- Clearly AI privacy policy ↗
- Clearly AI subprocessors ↗
Try Clearly AI
Visit the official website to get started with Clearly AI today.
Visit Clearly AI →